
Stop drowning in compliance complexity
Your auditor just asked how SOC 2 maps to ISO 27001. Your board wants a gap analysis by Friday. You're juggling six frameworks across three jurisdictions.
We've already mapped it. All 1,111 frameworks. 315K+ verified control connections. Instantly.
Get clarity where you're accountable. Try our Course Advisor →
Used by compliance teams at enterprises across healthcare, finance, government, and tech
One knowledge base, read from the standards themselves
1,111 frameworks, every requirement cited to its source
Not summaries scraped from the web. Each standard, regulation and code is read from the published text, split into its requirements, and every requirement carries the citation, the evidence an auditor asks for, and its judged links to the other frameworks. It grows every day as new editions are published and new frameworks are read. How this is built
Read from the text, not about it
Every requirement is our own statement of a clause of the published standard, cited so you can check it against the official text. When a framework is rebuilt it is read clause by clause, and a placeholder is never allowed to stand in for a requirement.
Browse the frameworks →Judged, with the refusals kept
A link between two frameworks is a judgement about evidence transfer, not a similarity score. Where a pair does not transfer, that refusal is recorded too, so a crosswalk you buy says what does not carry as clearly as what does.
See the crosswalks →Current editions, edition to edition
When a standard is revised the new edition is built beside the old one with the clause-by-clause lineage between them, so a team mid-transition can see exactly what moved.
What changed recently →Built on that knowledge base, a new tool every day
107 working tools, each free to run without an account
Paste the spreadsheet you already keep and get back the register, sheet or map a regulator or auditor asks for by name, with the exact clauses quoted. The newest are at the top; the full index is one page.
Regulatory Change Watch
Same-day alerts when a regulator page changes, with the controls to review and the clauses behind them..
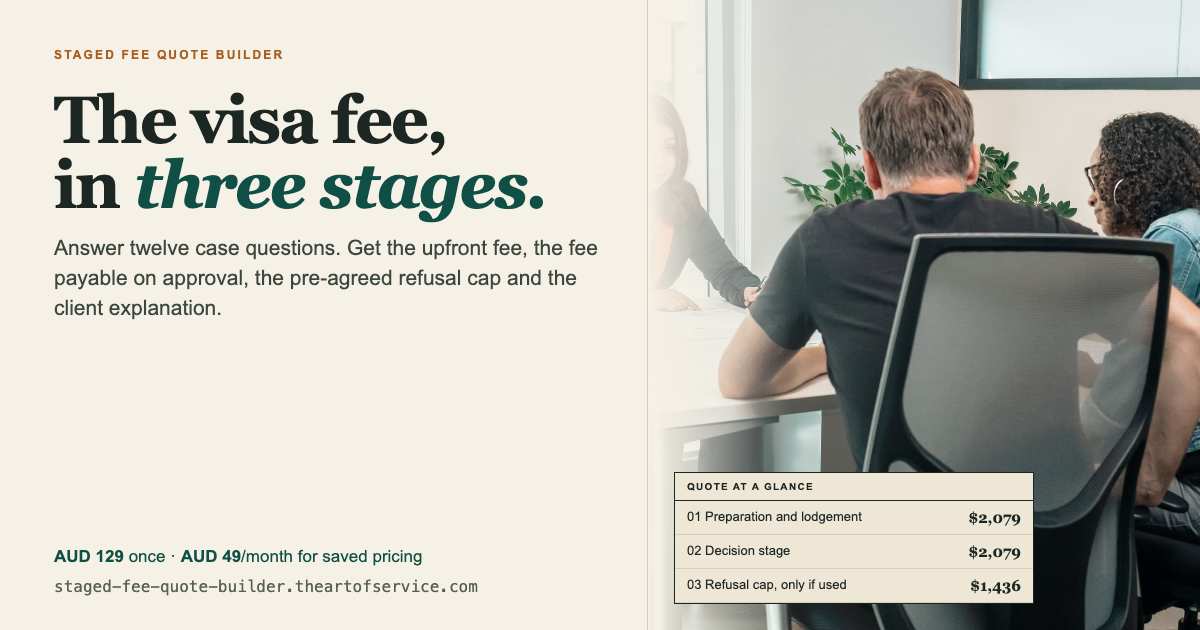
Staged Fee Quote Builder
Three-stage visa fee quotes: upfront, payable on approval, and a pre-agreed refusal cap..
Cyber Application Mapper
Read every question on a cyber application against SOC 2, ISO 27001, NIST 800-53, PCI DSS and the FTC Safeguards Rule, with the evidence to request..
Hearing Bundle Builder
Turn a dismissal timeline into the 21-day FWC deadline, a jurisdiction check, a Form F2 content draft, a chronology and an evidence index..
Questionnaire Freshness Register
Find the expired security questionnaire answer before the buyer does..
Export Royalty Estimator
Paste a defence or dual-use product list and get a dated, priced export-approval pathway sheet with a candidate classification and the cost band..
Referral Ask Scheduler
Turn a settled-loan list into a dated 12-month referral ask calendar with a personal script per client and milestone, and a tracker for who was asked and who referred.
State Compliance Checker
Paste a policy and see gaps against a US state's privacy act, breach notice statute, insurance data security rules and the HIPAA baseline, with the clause cited.
Budget Skew Auditor
Turns a pasted Meta or Google ads CSV into a ranked overspend and starvation report and a dated rebalance plan..
Looking for an older tool?
The front page shows the newest nine. The index lists all 107 with search and an A–Z sort.
New today · Data licensing
Content Feed self-serve checkout is live
1,111 frameworks, 50,882 controls, 315K+ cross-mappings, source-grounded. White-label rights. Click, pay, API key in seconds.
Sound familiar?
Compliance shouldn't feel like this
Weeks spent on manual control mapping
Get instant cross-framework mappings
Our AI maps controls between any two of 1,111 frameworks in seconds. What used to take your team weeks now takes one click.
$300/hr consultants for framework advice
AI-powered compliance intelligence for $149/mo
Ask questions, get gap analyses, build remediation plans. The expertise that used to require expensive consultants, now on-demand.
Siloed knowledge across your team
One source of truth for compliance
Framework guides, control libraries, comparison tools, and training courses. Everything your team needs in one connected platform.
How it works
From confused to compliant in three steps
Whether you're starting from scratch or managing multi-framework compliance, here's how we get you there.
See the full picture
Search 1,111 frameworks. Compare any two side-by-side. Instantly see which controls overlap and where the gaps are.
Browse FrameworksLet AI do the heavy lifting
Our platform maps controls automatically, generates gap analyses, and builds prioritised remediation plans, work that used to take weeks.
Try the PlatformBuild your team's expertise
Close knowledge gaps with executive education courses. Earn professional certifications recognised across 160+ countries.
View CoursesFree Assessment
How ready is your organization for compliance?
Answer 7 questions and get your personalized Compliance Readiness Score, complete with a radar chart, key insights, and an action plan across 5 dimensions.
Get Your ScoreStart exploring
The frameworks your auditor is asking about
Deep guides with controls, domains, and instant cross-framework mapping.
ISO 27001:2013
Information technology, security techniques, information security management systems, requirements: the second edition (2013-10-01), superseded by ISO/IEC 27001:2022. The transition period for certificates to this edition ended on 31 October 2025; it is kept for lineage and for the 2013 to 2022 edition crosswalks.
SOC 2
Trust Service Criteria for service organizations covering security, availability, processing integrity, confidentiality, and privacy.
NIST Cybersecurity Framework 1.0
NIST's Framework for Improving Critical Infrastructure Cybersecurity, Version 1.0 (February 2014): the five Functions, 22 Categories and 98 Subcategories in the Version 1.0 wording, each marked as kept or reworded in Version 1.1. Superseded in April 2018; kept for historic assessments and contracts that cite it.
GDPR
General Data Protection Regulation - EU regulation on data protection and privacy for all individuals within the European Union and European Economic Area.
HIPAA Breach Notification Rule
HIPAA Breach Notification Rule standards for breach risk assessment and notification to individuals, the media, HHS and covered entities by business associates.
PCI DSS v4.0
PCI DSS v4.0 is the global security standard for organisations that store, process, or transmit cardholder data, published by the PCI Security Standards Council. Version 4.0, released in March 2022 with full enforcement from 31 March 2025, introduced a customised approach to validation, expanded multi-factor authentication requirements, and added 64 new requirements. It contains 249 controls across 12 requirement areas.
Built for you
Whether you're a team of one or one hundred
Compliance Officers
Map controls across frameworks instantly. Stop building spreadsheets, start building strategy.
CISOs & Risk Leaders
Board-ready gap analyses in minutes. See your multi-framework landscape at a glance.
Consultants & Advisors
Serve more clients with less effort. Instant framework intelligence at your fingertips.
Teams & Enterprises
Upskill your entire team with professional certification courses trusted in 160+ countries.
Implementation Guides
Step-by-step compliance guidance
From the Blog
Latest compliance insights
What Is an Enterprise Service Bus (ESB)? A Practitioner’s Guide
An enterprise service bus (ESB) is a middleware architecture that enables reliable, scalable integration across disparate systems using a common communication backbone.
Cybersecurity TrainingWhat Is an AI-Powered Security Automation Seminar?
An AI-powered security automation seminar is a training event that teaches professionals how to use artificial intelligence to enhance threat detection, response, and compliance workflows in cybersecurity.
Regulatory ComplianceWhat Are Regulatory Artwork Competencies?
Regulatory artwork competencies are the skills and knowledge required to ensure product labels, packaging, and promotional materials comply with legal and industry standards.
Questions people ask
What is The Art of Service?
The Art of Service is a compliance education and framework intelligence company based in Brisbane, Australia, founded by Ivanka Menken and Gerard Blokdyk. It publishes professional courses, implementation playbooks and toolkits, and runs a compliance platform that maps controls across regulatory frameworks so an organisation can reuse evidence it already holds.
What is a compliance framework?
A compliance framework is a structured set of guidelines, controls, and best practices that organisations follow to meet regulatory requirements, manage risk, and demonstrate due diligence. Examples include ISO 27001 for information security, SOC 2 for service organisations, and NIST CSF for cybersecurity.
How many compliance frameworks does The Art of Service cover?
The Art of Service covers 1,111 compliance frameworks across information security, privacy, governance, risk management, cloud security, financial services, healthcare, and more. Each framework page includes an overview, key controls, related frameworks, and links to cross-framework control mappings.
What is the difference between ISO 27001 and SOC 2?
ISO 27001 is an international standard for Information Security Management Systems (ISMS) that results in a certificate valid for three years. SOC 2 is a North American auditing standard for service organisations that produces an attestation report, typically renewed annually. Many organisations pursue both to satisfy global and US-specific customer requirements.
How much does compliance training cost?
The Art of Service offers a free tier for its compliance intelligence platform. Professional plans start at $149/month, providing access to 1,111 frameworks, 315K+ verified control mappings, and AI-powered advisory. Individual courses and self-assessment toolkits are available separately through the Academy and Store.
Can AI help with compliance?
Yes. AI-powered compliance tools can automate control mapping across frameworks, identify gaps in your compliance posture, generate audit-ready documentation, and keep you updated on regulatory changes. The Art of Service platform uses AI trained on 25 years of compliance expertise to provide framework-specific guidance.
From our co-founder
Ivanka Menken co-founded The Art of Service and now mentors founders of growing businesses through cash, pricing and letting-go decisions. Her book The Clarity Shift is free, with no email required.
Your next audit doesn't have to be painful
Join 100,000+ professionals who replaced compliance chaos with clarity.
Free tier available. No credit card required. Set up in 2 minutes.