
Stop drowning in compliance complexity
Your auditor just asked how SOC 2 maps to ISO 27001. Your board wants a gap analysis by Friday. You're juggling six frameworks across three jurisdictions.
We've already mapped it. All 685 frameworks. 307K+ verified control connections. Instantly.
Get clarity where you're accountable. Try our Course Advisor →
Used by compliance teams at enterprises across healthcare, finance, government, and tech
One knowledge base, read from the standards themselves
685 frameworks, every requirement cited to its source
Not summaries scraped from the web. Each standard, regulation and code is read from the published text, split into its requirements, and every requirement carries the citation, the evidence an auditor asks for, and its judged links to the other frameworks. It grows every day as new editions are published and new frameworks are read.
Read from the text, not about it
The corpus behind the graph is the standards themselves. When a framework is rebuilt it is read clause by clause against the copy held, and a placeholder is never allowed to stand in for a requirement.
Browse the frameworks →Judged, with the refusals kept
A link between two frameworks is a judgement about evidence transfer, not a similarity score. Where a pair does not transfer, that refusal is recorded too, so a crosswalk you buy says what does not carry as clearly as what does.
See the crosswalks →Current editions, edition to edition
When a standard is revised the new edition is built beside the old one with the clause-by-clause lineage between them, so a team mid-transition can see exactly what moved.
What changed recently →Built on that knowledge base, a new tool every day
9 working tools, each free to run without an account
Paste the spreadsheet you already keep and get back the register, sheet or map a regulator or auditor asks for by name, with the exact clauses quoted. The newest is at the top.
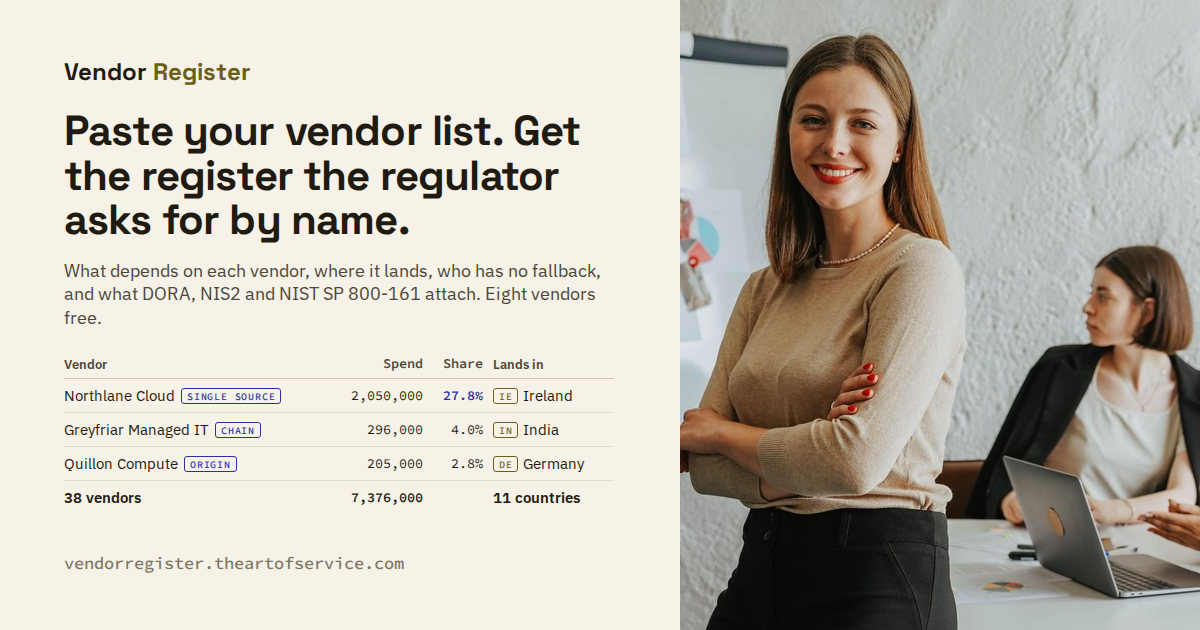
Vendor Register
Paste your vendor list, get what you depend on each vendor for, where the dependency lands, and the register DORA and NIS2 ask for.
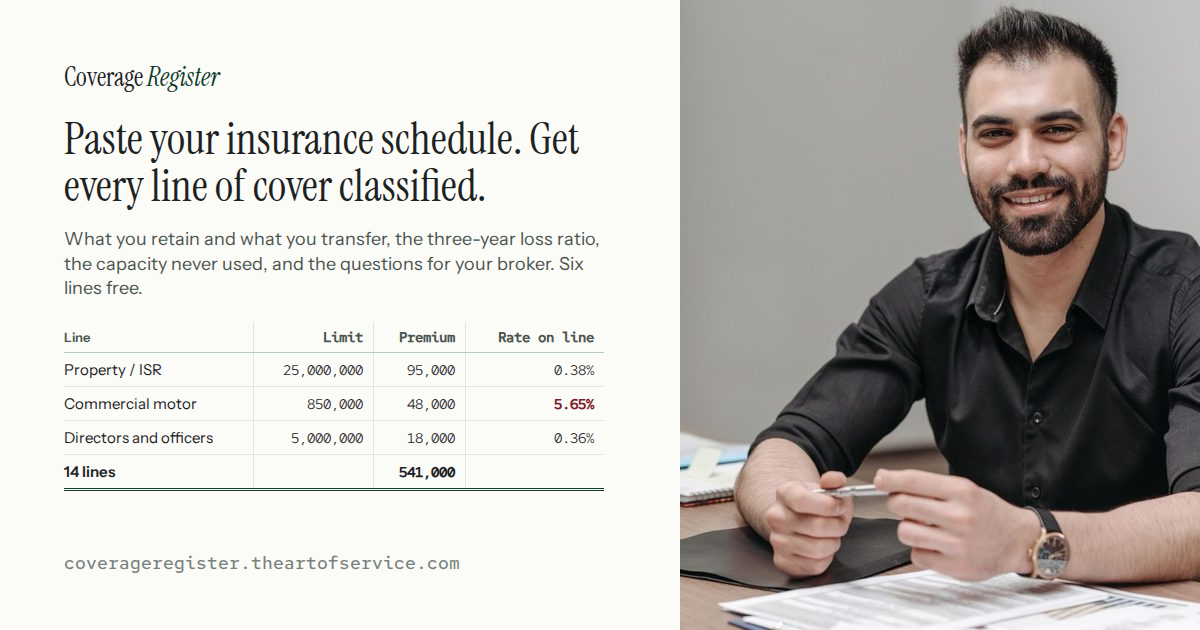
Coverage Register
Paste your insurance schedule and see what you retain, what you transfer, and what you pay for and never use.
Handoff Register
Paste a process, see which steps a person still re-keys and which could be handed over.
Conformity Sheet
Paste your product list, get the regulations, documents and after-sale duties per product and market.
Maintenance Log Converter
Paste your maintenance schedule or log, get every item as a condition-based check with the evidence it produces.
Agent Register
Paste the AI agents and copilots your teams use, get each one classified for what it can act on and reach.
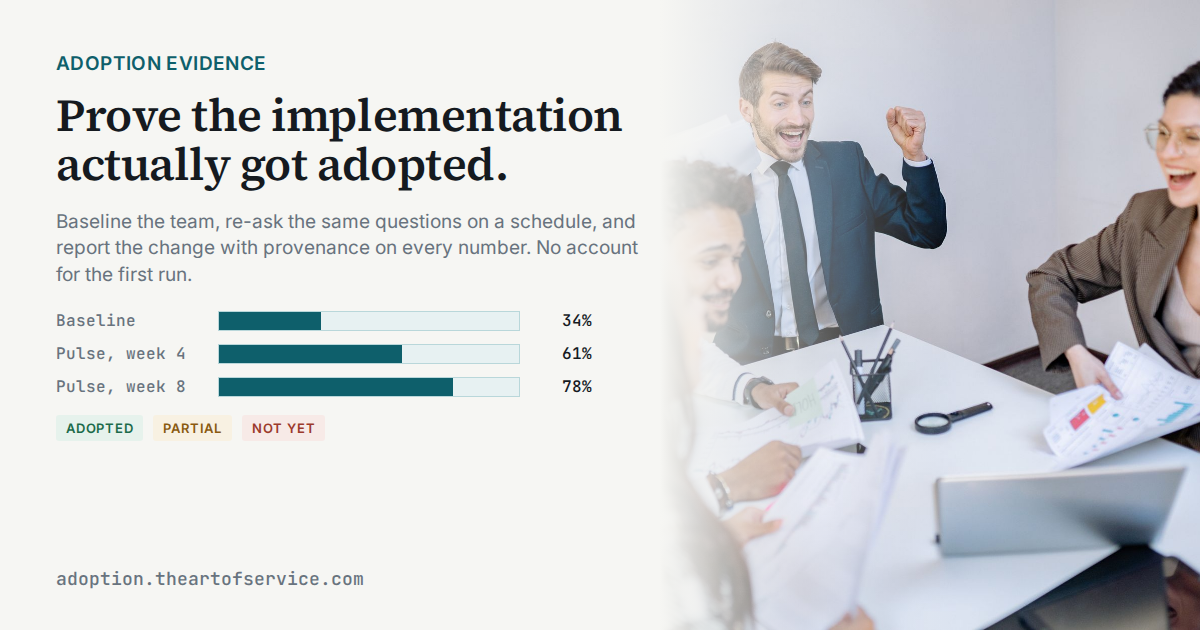
Adoption Evidence
Baseline, pulse and report whether an implementation actually got adopted, with provenance on every number.
Field Register
Paste your CRM field list, get each field classified for personal data, lawful basis and AI use.
Evidence Sheet
Paste your control spreadsheet, get the evidence auditors ask for per control.
New today · Data licensing
Content Feed self-serve checkout is live
685 frameworks, 23,728 controls, 307K+ cross-mappings, source-grounded. White-label rights. Click, pay, API key in seconds.
Sound familiar?
Compliance shouldn't feel like this
Weeks spent on manual control mapping
Get instant cross-framework mappings
Our AI maps controls between any two of 685 frameworks in seconds. What used to take your team weeks now takes one click.
$300/hr consultants for framework advice
AI-powered compliance intelligence for $149/mo
Ask questions, get gap analyses, build remediation plans. The expertise that used to require expensive consultants, now on-demand.
Siloed knowledge across your team
One source of truth for compliance
Framework guides, control libraries, comparison tools, and training courses. Everything your team needs in one connected platform.
How it works
From confused to compliant in three steps
Whether you're starting from scratch or managing multi-framework compliance, here's how we get you there.
See the full picture
Search 685 frameworks. Compare any two side-by-side. Instantly see which controls overlap and where the gaps are.
Browse FrameworksLet AI do the heavy lifting
Our platform maps controls automatically, generates gap analyses, and builds prioritised remediation plans, work that used to take weeks.
Try the PlatformBuild your team's expertise
Close knowledge gaps with executive education courses. Earn professional certifications recognised across 160+ countries.
View CoursesFree Assessment
How ready is your organization for compliance?
Answer 7 questions and get your personalized Compliance Readiness Score, complete with a radar chart, key insights, and an action plan across 5 dimensions.
Get Your ScoreStart exploring
The frameworks your auditor is asking about
Deep guides with controls, domains, and instant cross-framework mapping.
ISO 27001:2022
International standard for establishing, implementing, maintaining and continually improving an information security management system (ISMS).
SOC 2
Trust Service Criteria for service organizations covering security, availability, processing integrity, confidentiality, and privacy.
NIST Cybersecurity Framework 2.0
Voluntary framework for managing and reducing cybersecurity risk, organized around six core functions.
GDPR
General Data Protection Regulation - EU regulation on data protection and privacy for all individuals within the European Union and European Economic Area.
HIPAA Security Rule
Health Insurance Portability and Accountability Act security standards for protecting electronic protected health information (ePHI).
PCI DSS v4.0
PCI DSS v4.0 is the global security standard for organisations that store, process, or transmit cardholder data, published by the PCI Security Standards Council. Version 4.0, released in March 2022 with full enforcement from 31 March 2025, introduced a customised approach to validation, expanded multi-factor authentication requirements, and added 64 new requirements. It contains 249 controls across 12 requirement areas.
Built for you
Whether you're a team of one or one hundred
Compliance Officers
Map controls across frameworks instantly. Stop building spreadsheets, start building strategy.
CISOs & Risk Leaders
Board-ready gap analyses in minutes. See your multi-framework landscape at a glance.
Consultants & Advisors
Serve more clients with less effort. Instant framework intelligence at your fingertips.
Teams & Enterprises
Upskill your entire team with professional certification courses trusted in 160+ countries.
Implementation Guides
Step-by-step compliance guidance
From the Blog
Latest compliance insights
ISO 55000 Online Training: What You Get and Who It's For
Comprehensive ISO 55000 online training is available covering asset management systems implementation, audit readiness, and practical application for practitioners.
business managementPlumbing Business Management: How to Run a Profitable, Compliant Operation
Plumbing business management involves balancing field operations, customer service, compliance, and financial controls to sustain growth and avoid regulatory risk.
technology integrationEnterprise Service Bus (ESB): What It Is and Where It Fails in Practice
An enterprise service bus (ESB) integrates disparate systems using middleware to route, transform, and manage messages, but its complexity often undermines reliability and maintainability.
Questions people ask
What is The Art of Service?
The Art of Service is a compliance education and framework intelligence company based in Brisbane, Australia, founded by Ivanka Menken and Gerard Blokdyk. It publishes professional courses, implementation playbooks and toolkits, and runs a compliance platform that maps controls across regulatory frameworks so an organisation can reuse evidence it already holds.
What is a compliance framework?
A compliance framework is a structured set of guidelines, controls, and best practices that organisations follow to meet regulatory requirements, manage risk, and demonstrate due diligence. Examples include ISO 27001 for information security, SOC 2 for service organisations, and NIST CSF for cybersecurity.
How many compliance frameworks does The Art of Service cover?
The Art of Service covers 685 compliance frameworks across information security, privacy, governance, risk management, cloud security, financial services, healthcare, and more. Each framework page includes an overview, key controls, related frameworks, and links to cross-framework control mappings.
What is the difference between ISO 27001 and SOC 2?
ISO 27001 is an international standard for Information Security Management Systems (ISMS) that results in a certificate valid for three years. SOC 2 is a North American auditing standard for service organisations that produces an attestation report, typically renewed annually. Many organisations pursue both to satisfy global and US-specific customer requirements.
How much does compliance training cost?
The Art of Service offers a free tier for its compliance intelligence platform. Professional plans start at $149/month, providing access to 685 frameworks, 307K+ verified control mappings, and AI-powered advisory. Individual courses and self-assessment toolkits are available separately through the Academy and Store.
Can AI help with compliance?
Yes. AI-powered compliance tools can automate control mapping across frameworks, identify gaps in your compliance posture, generate audit-ready documentation, and keep you updated on regulatory changes. The Art of Service platform uses AI trained on 25 years of compliance expertise to provide framework-specific guidance.
Your next audit doesn't have to be painful
Join 100,000+ professionals who replaced compliance chaos with clarity.
Free tier available. No credit card required. Set up in 2 minutes.